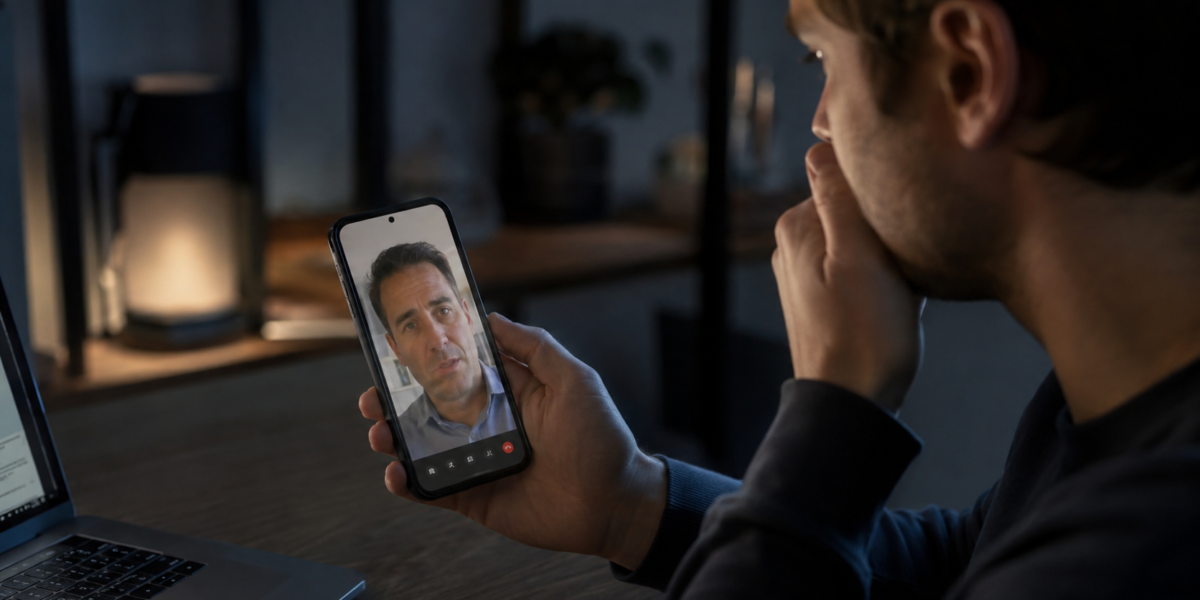
A familiar voice asks for money.
A video call appears to show your manager authorizing a transfer.
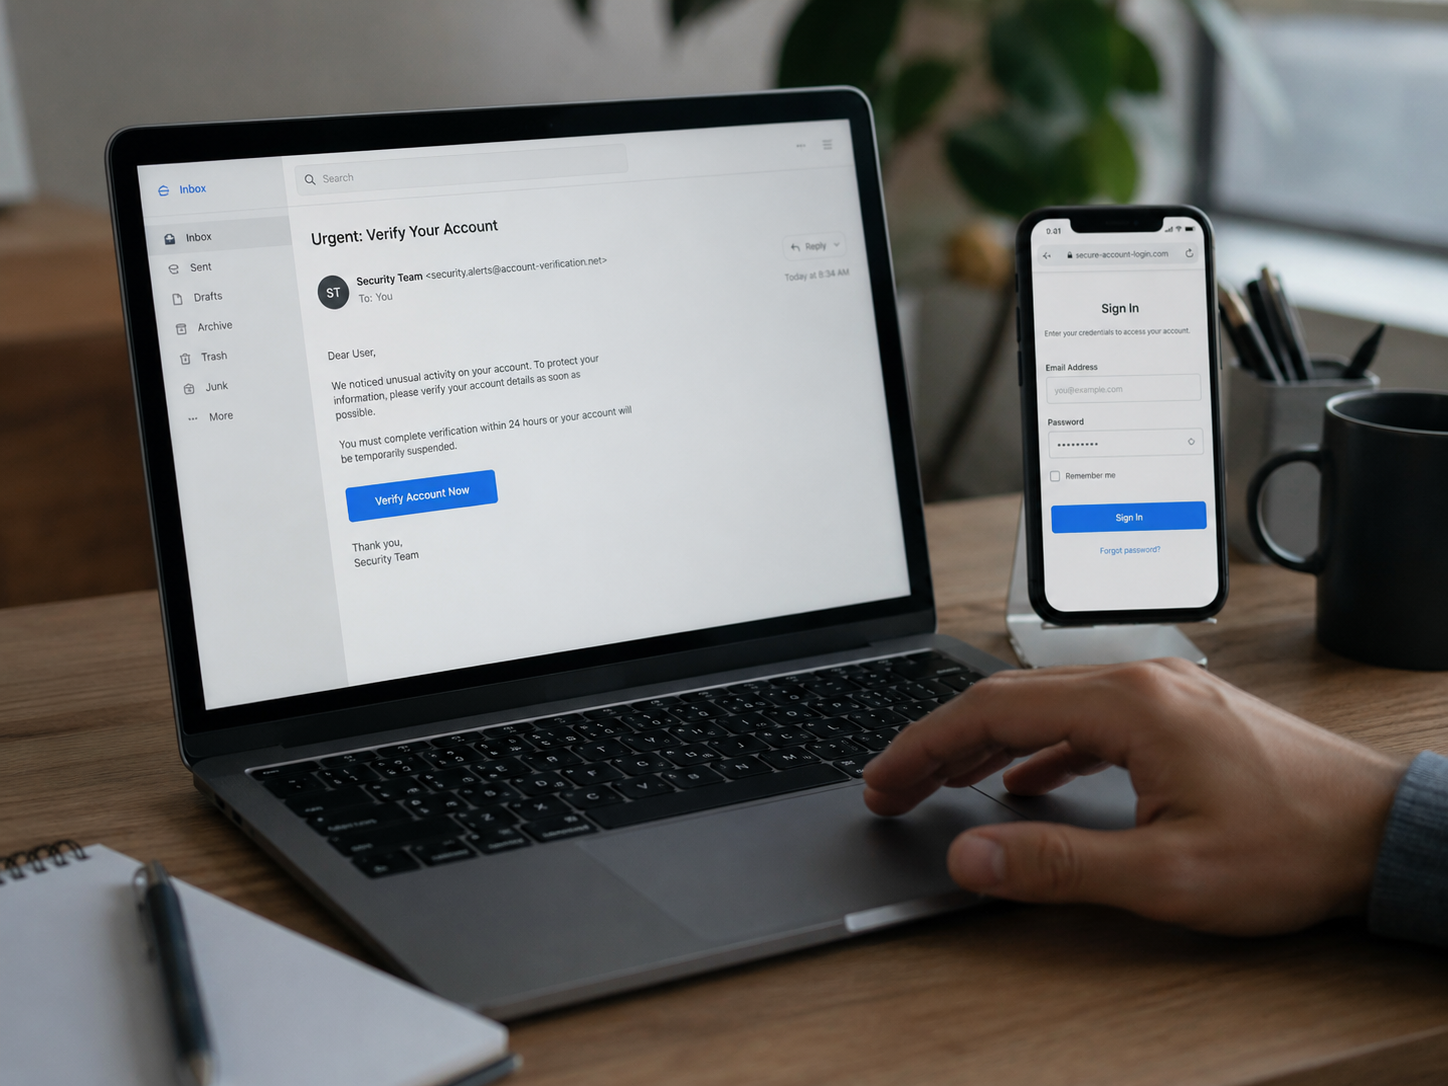
An email from a company you use contains perfect grammar, correct branding and information that appears to be personally relevant.
A photograph shows a product that does not exist.
None of these elements can now be considered proof that the person, message or object is real.
Artificial intelligence has changed fraud by making convincing impersonation cheaper, faster and easier to scale.
The 2026 INTERPOL Global Financial Fraud Threat Assessment describes financial fraud as one of the world’s fastest-evolving transnational crimes and estimates that AI-enhanced fraud can be 4.5 times more profitable than traditional fraud methods. The organization also warns that generative AI, deepfakes and increasingly autonomous systems are being integrated into complete fraud operations.
The financial numbers already indicate the scale of the problem. The US Federal Trade Commission recorded approximately $16 billion in reported fraud losses during 2025, around 25% more than in 2024. Impersonation scams alone accounted for approximately $3.5 billion.
AI did not invent fraud.
It removed several of its previous limitations.
What are AI scams?
An AI scam is a fraud in which artificial intelligence is used to create, improve, automate or personalize part of the deception.
AI can help criminals generate:
- realistic emails;
- cloned voices;
- fake photographs;
- synthetic video;
- fake identities;
- personalized messages;
- fraudulent advertisements;
- convincing websites;
- automated conversations;
- fake customer-support interactions.
The underlying objective is usually familiar:
money, credentials, personal information or access to an account.
What has changed is the quality and scale of the deception.
Traditional phishing frequently contained obvious signals: poor spelling, generic text, strange formatting or messages that made little contextual sense.
Generative AI can eliminate many of those weaknesses.
A scammer can now produce fluent communications in multiple languages, adapt them to a specific company or person and maintain believable conversations for extended periods.
Pattern detected: poor grammar is no longer a reliable phishing detector.
Why AI scams are becoming more dangerous in 2026
AI reduces the amount of effort required to manufacture credibility.
Microsoft Threat Intelligence reported in March 2026 that threat actors were using generative AI to accelerate several stages of cyber operations, including writing phishing messages, translating material, processing stolen information and generating supporting code and infrastructure. Microsoft described AI primarily as a force multiplier: humans continue to define the objectives while AI makes execution faster and easier to scale.
INTERPOL has identified a similar evolution.
Its 2026 assessment reports the appearance of Deepfake-as-a-Service offerings that package synthetic identities, generated video avatars, voice cloning and other capabilities for criminal use. The report warns that increasingly convincing digital clones can be produced from limited source material collected online.
This changes the economics of deception.
Previously, creating a convincing false identity required:
- writing ability;
- language knowledge;
- graphic design;
- video editing;
- social engineering experience;
- significant manual interaction.
AI can automate parts of all of them.
The main types of AI scams in 2026
Several patterns currently deserve particular attention.
1. AI voice cloning scams
Voice cloning can reproduce the characteristics of someone’s speech from relatively short recordings.
Those recordings may come from:
- Instagram;
- TikTok;
- YouTube;
- podcasts;
- WhatsApp audio;
- interviews;
- company presentations;
- public videos.
The result can then be used during a telephone call or inside a generated audio message.
The victim hears a familiar voice.
That creates immediate trust.
A real case in Spain: the cloned daughter
In February 2026, Spain’s National Cybersecurity Institute, INCIBE, documented a case involving an older woman who received a call claiming that her daughter required urgent surgery.
A supposed healthcare worker explained the situation and then passed the phone to the daughter.
The woman heard what appeared to be her daughter’s voice crying and asking for help.
The voice had apparently been cloned using AI.
The objective was to make the victim pay for the alleged emergency operation.
The important detail is not the quality of the audio.
It is the structure of the attack:
Trusted identity
↓
Emotional shock
↓
Urgency
↓
Reduced time to verify
↓
Payment request
AI reinforces the first stage.
Social engineering does the rest.
2. The AI CEO scam
Companies face a similar threat.
Instead of impersonating a family member, criminals impersonate:
- CEOs;
- CFOs;
- managers;
- suppliers;
- important customers.
INCIBE documented another Spanish case in February 2026 in which customers of a business owner received telephone calls apparently using his cloned voice.
The callers instructed customers to begin sending payments to a different bank account.
Several customers detected the anomaly because the telephone number had changed and contacted the real business owner through another channel before transferring money.
That verification step prevented the attack from becoming a successful payment diversion.
This is one of the most important defensive principles in the AI era:
A familiar voice does not authenticate a financial instruction.
3. Deepfake video scams
Deepfake video adds another layer of credibility.
AI can increasingly manipulate or synthesize:
- faces;
- voices;
- facial movements;
- environments;
- gestures;
- entire people.
This allows criminals to fabricate videos apparently featuring executives, celebrities, family members or authorities.
More sophisticated systems can also modify video and audio in near real time.
A video call is therefore no longer absolute proof of identity.
Can you detect a deepfake by looking at the image?
Sometimes.
But this approach is becoming progressively less reliable.
Older deepfakes often contained obvious defects:
- unnatural blinking;
- distorted hands;
- inconsistent teeth;
- strange reflections;
- incorrect shadows;
- unstable facial boundaries;
- lip-sync problems;
- changes between frames.
These anomalies can still appear.
They should be treated as warning signals, not as a detection system.
INCIBE notes that improvements in generative technology are making edited content increasingly difficult to distinguish from genuine material.
A convincing deepfake may contain none of the classic visual defects.
The safest question is therefore not:
Does this video look fake?
It is:
Can I independently verify that this communication is real?
That is a different security model.
4. AI-generated product and marketplace scams
Synthetic media does not need to impersonate a person.
It can also create evidence of objects that do not exist.
INCIBE documented an unusually clear example in Spain in March 2026.
An agricultural company purchased a tractor through a foreign website for more than €100,000.
The seller supplied photographs showing the tractor from different angles and videos apparently showing it loaded for transport.
The buyer therefore believed that the machine existed and had been dispatched.
It never arrived.
After reviewing the material more carefully, inconsistencies revealed that the supporting images and videos had been generated using AI.
This illustrates a new problem for online commerce.
Photographs are evidence of pixels.
They are no longer necessarily evidence of an object.
5. AI-enhanced phishing
Phishing remains one of the most effective forms of digital fraud.
AI makes it easier to remove many of the characteristics people have traditionally been taught to look for.
A modern phishing message can have:
- perfect grammar;
- professional formatting;
- correct terminology;
- personalized information;
- an appropriate tone;
- convincing branding.
It may even reference information extracted from social networks, company websites or previous data breaches.
The absence of spelling mistakes means very little.
Real phishing campaigns detected in 2026
Microsoft documented several relevant campaigns during 2026.
In May, researchers detected phishing messages impersonating ChatGPT and claiming that users needed to update their payment method to prevent their Plus subscription from being downgraded.
Microsoft observed 4,500 emails in one part of the campaign targeting South Africa and broader related activity capable of distributing up to 100,000 emails in a single day across markets including Switzerland, Austria and South Africa.
The destination pages attempted to collect payment and personal information.
The same Microsoft investigation found another campaign impersonating Anthropic and Claude that targeted users at more than 2,000 organizations in April 2026.
Its message was different.
Instead of requesting payment, it claimed that the user’s account had violated acceptable-use policies and required an appeal.
Different narrative.
Same mechanism:
Recognizable brand
↓
Plausible problem
↓
Urgency
↓
External interaction
↓
Credential / payment theft
AI itself is now used as phishing bait
One of the more unusual patterns of 2026 is that criminals are using the popularity of AI products themselves to distribute malware and steal credentials.
Microsoft has observed campaigns impersonating brands including:
- ChatGPT;
- Microsoft Copilot;
- Claude;
- DeepSeek.
In another April 2026 case, attackers created a fraudulent GitHub presence advertising fake DeepSeek V4 installers that delivered information-stealing malware.
Search engines helped expose users to the fraudulent repository before it was removed.
The product does not need to be compromised.
The brand only needs to be trusted.
6. More advanced phishing can bypass traditional MFA
A phishing page does not always need to steal a password.
Modern attacks increasingly target authentication sessions themselves.
Microsoft reported a large campaign in April 2026 using adversary-in-the-middle techniques that targeted more than 35,000 users across 13,000 organizations in 26 countries.
These attacks can intercept authentication traffic and potentially defeat conventional forms of multifactor authentication that are not phishing-resistant.
Another AI-enabled campaign documented by Microsoft used automation around device-code authentication, legitimate cloud infrastructure and dynamically generated attack components to make phishing infrastructure more adaptable.
The defensive implication is important.
MFA remains essential.
But not all MFA mechanisms provide the same protection against phishing.
Passkeys and other phishing-resistant authentication mechanisms provide stronger protection than authentication flows that depend on codes a user can be persuaded to approve or enter.
7. AI romance scams and synthetic identities
Romance fraud becomes more scalable when the criminal no longer needs a consistent real identity.
AI can generate:
- profile photographs;
- messages;
- personal histories;
- audio;
- video;
- continuous conversation.
The scammer can maintain a synthetic persona over time.
INTERPOL’s 2026 assessment warns that AI-generated personas and deepfake content are increasingly being combined with romance fraud and financially motivated sextortion.
A video call should therefore no longer be treated as definitive proof that an online identity corresponds to a real individual.
8. AI-generated emergency scams
Emergency scams exploit one of the most effective vulnerabilities in human decision-making:
time pressure combined with emotion.
Typical narratives include:
- a family member has been arrested;
- someone has been injured;
- urgent medical treatment is required;
- a wallet or phone has been stolen;
- a payment must be made immediately;
- someone is trapped abroad.
Voice cloning makes these stories considerably more convincing.
The FTC explicitly advises consumers not to trust the voice itself, even when it sounds exactly like a relative. Instead, the person should be contacted using a telephone number already known to be genuine.
The anatomy of an AI scam
Despite technological changes, most successful attacks continue to exploit a predictable chain.
Stage 1: information gathering
The attacker collects information from:
- social networks;
- websites;
- public records;
- leaked databases;
- company pages;
- videos;
- previous compromises.
AI can accelerate this analysis.
Stage 2: identity construction
The attacker creates or impersonates a credible identity.
This could involve:
- an email address;
- a cloned voice;
- synthetic photographs;
- a fake website;
- a deepfake video;
- a social profile.
Stage 3: contextual credibility
The message contains information that makes it believable.
For example:
We need to change the bank account for invoice 1843.
This is significantly more persuasive if invoice 1843 actually exists.
Stage 4: pressure
The attacker introduces urgency.
Common phrases include:
- immediately;
- confidential;
- today only;
- final warning;
- account suspended;
- urgent medical situation;
- don’t tell anyone;
- CEO request.
Urgency reduces verification.
Stage 5: the irreversible action
The final objective appears:
- transfer money;
- enter credentials;
- disclose a verification code;
- install software;
- connect a wallet;
- purchase cryptocurrency;
- share sensitive information.
This is normally the most useful moment to stop the attack.
How to recognize an AI scam in 2026
There is no universal visual detector.
A better strategy is to analyse behavior and context.
Watch for combinations of these signals.
Unexpected urgency
Someone is demanding an immediate action.
The shorter the permitted verification window, the more suspicious the situation becomes.
A change in normal procedure
Examples:
- new bank account;
- new phone number;
- unusual payment method;
- unexpected login page;
- new communication channel;
- request to bypass established approval.
Changes in process are often more revealing than flaws in the generated media.
Secrecy
Statements such as:
Don’t tell anyone.
This is confidential.
Do not contact the bank.
Don’t call me back.
should significantly increase suspicion.
Isolation prevents independent verification.
Financial instructions delivered through informal channels
A WhatsApp message, video call or recognizable voice should not override established financial procedures.
Requests for difficult-to-reverse payments
Particular caution is required with requests involving:
- cryptocurrency;
- gift cards;
- rapid wire transfers;
- unusual payment services.
Fraud relies heavily on payment mechanisms that are difficult to reverse.
Unexpected authentication requests
Do not approve an MFA notification, enter a device code or authorize a login simply because someone claiming to be IT support asks you to do so.
Inconsistent context
The voice may be perfect while the story is wrong.
Check:
- location;
- schedule;
- terminology;
- usual communication style;
- normal approval process;
- bank information;
- known contact details.
Context remains difficult to counterfeit perfectly.
The most effective deepfake detector is another communication channel
Imagine receiving a video call from your CFO.
The person looks correct.
The voice is correct.
They know about a real supplier.
They request an urgent €40,000 transfer.
Trying to determine whether the face contains visual artifacts is the wrong security control.
Instead:
- end the call;
- use the CFO’s previously known telephone number;
- contact them independently;
- confirm the request;
- follow the organization’s normal financial approval procedure.
If the original call was real, the additional verification costs a few minutes.
If it was fake, the verification breaks the attack.
Observation recorded: authenticity should increasingly be verified through systems and procedures rather than human perception alone.
A simple protection protocol: STOP — SWITCH — VERIFY
A useful rule for suspected AI scams is:
STOP
Do not react immediately.
Urgency is part of the attack.
SWITCH
Move to another communication channel.
If the request arrived by:
- email → call;
- phone → message a known number;
- WhatsApp → call directly;
- video → contact through the company’s internal system.
Do not use contact details supplied inside the suspicious communication.
VERIFY
Confirm both:
identity
and
request.
A real person can confirm both through an independent channel.
This protocol remains effective whether the attacker uses text, audio, images or video.
How families can protect themselves from voice cloning scams
Families can establish simple procedures before an emergency occurs.
For example:
- define a private verification question or phrase;
- verify emergency requests through another relative;
- call the supposed victim directly;
- never transfer money solely because a voice sounds familiar;
- treat requests for secrecy as suspicious.
Public audio should also be considered part of a person’s digital footprint.
Voice is no longer an effective secret.
How companies should protect themselves
Businesses require stronger procedural controls because the potential financial exposure is significantly higher.
Never authenticate a payment by voice alone
A CEO’s voice is not a security credential.
Neither is their face.
Require secondary verification for bank-detail changes
Changing a supplier’s bank account should require confirmation through a previously established contact channel.
Use multi-person approval for significant transactions
One compromised employee should not be able to authorize a high-value transfer simply because an apparently senior executive requested it.
Use phishing-resistant authentication
Organizations should progressively move toward:
- passkeys;
- FIDO2 security keys;
- certificate-based authentication;
- other phishing-resistant mechanisms.
Microsoft specifically recommends phishing-resistant MFA as part of its 2026 identity-security strategy.
Protect executive media exposure
Executives with large quantities of public:
- video;
- podcasts;
- conference presentations;
- interviews;
provide useful material for impersonation.
This does not mean they should disappear from public communication.
It means companies should assume that their voices and faces can potentially be replicated.
Establish an out-of-band verification policy
Employees should know exactly what to do when receiving unusual requests from executives.
This removes an important social-engineering weapon:
uncertainty.
What should you do if you have already sent money?
Speed becomes important.
Do not continue interacting with the suspected scammer.
Immediately:
- contact your bank or payment provider;
- explain that the transaction resulted from suspected fraud;
- request reversal or blocking where possible;
- preserve messages, numbers, emails, screenshots and payment information;
- change compromised credentials;
- revoke suspicious sessions;
- report the incident to the appropriate authorities.
For users and companies in Spain, INCIBE operates the 017 cybersecurity helpline and recommends preserving evidence and reporting identity fraud to law enforcement.
If credentials have been disclosed, assume that the account may already be compromised rather than waiting for visible evidence.
What should you do if you clicked a phishing link?
Clicking does not always mean an account has been compromised.
What happened afterward matters.
If you entered a password
Change it immediately from the legitimate service.
If the same password is reused elsewhere, change those accounts as well.
If you approved an MFA request
Review active sessions and revoke unknown ones.
If you downloaded software
Disconnect the affected device from sensitive systems and perform an appropriate security assessment.
If you provided bank information
Contact the financial institution.
If nothing was entered or downloaded
Close the site and report the message, while remaining alert for follow-up attempts.
Can AI detect AI-generated scams?
Sometimes.
AI is increasingly used on both sides.
Security systems can analyse:
- email behaviour;
- suspicious domains;
- login anomalies;
- malicious attachments;
- unusual account activity;
- synthetic media signals;
- transaction anomalies.
But a universal detector capable of labeling every image, video or voice as real or AI-generated does not currently provide a reliable security boundary.
Detection remains an arms race.
Generation improves.
Detection adapts.
Generation changes again.
For high-consequence decisions, procedural verification remains more reliable than asking a detector whether something was generated by AI.
AI scams are not just deepfakes
It is easy to reduce the subject to fake video.
That misses the larger transformation.
AI can participate at almost every stage:
Target research
↓
Personalized phishing
↓
Synthetic identity
↓
Automated conversation
↓
Voice / video impersonation
↓
Payment request
↓
Follow-up manipulation
The most effective attack may contain no obvious deepfake at all.
A perfectly written personalized email can be enough.
The scale of AI-related fraud is becoming measurable
The FBI’s 2025 Internet Crime Report recorded 22,364 complaints containing AI-related information, associated with more than $893 million in adjusted losses.
The FBI reported that businesses lost more than $30 million in AI-related Business Email Compromise cases alone, while AI-associated distress scams generated more than $5 million in reported losses.
These figures do not mean every case was created entirely by AI.
They indicate that AI is increasingly becoming part of existing fraud mechanisms.
That distinction matters.
Fraud is not being replaced.
It is being augmented.
Social media is becoming part of the attack infrastructure
Social media provides criminals with two resources:
distribution
and
intelligence about the victim.
The FTC reported that almost 30% of people who said they lost money to fraud in 2025 indicated that the scam began on social media. Reported losses from social-media-originated scams reached approximately $2.1 billion.
AI can make use of the information people voluntarily publish:
- relatives;
- workplaces;
- holidays;
- job titles;
- colleagues;
- interests;
- photographs;
- voices;
- routines.
The result is more targeted social engineering.
A message no longer needs to look generic.
It can look specifically designed for you.
Because it may be.
The rules of digital trust are changing
For most of the internet era, humans used several informal signals to establish authenticity.
Seeing someone provided confidence.
Hearing someone’s voice provided confidence.
Correct writing provided confidence.
A photograph provided evidence.
Each of those assumptions has weakened.
Synthetic media does not mean that nothing can be trusted.
It means trust needs to move toward stronger signals.
From:
I recognize this person.
Toward:
I verified this person through an independent trusted channel.
From:
The email looks professional.
Toward:
The domain, request and destination are correct.
From:
I saw the product in a video.
Toward:
The seller, transaction and asset have been independently verified.
This is a structural change.
Frequently asked questions about AI scams
What are AI scams?
AI scams are fraudulent schemes that use artificial intelligence to create or improve deceptive content, impersonate people, automate conversations, personalize phishing or manufacture convincing images, audio and video.
What is a deepfake scam?
A deepfake scam uses AI-generated or manipulated audio, video or images to make a victim believe that a real person said or did something that never occurred.
Can AI clone someone’s voice?
Yes. Modern voice-generation systems can reproduce recognizable characteristics of a person’s speech from recorded material. Public videos, podcasts and social media can potentially provide source audio.
How can I tell if a voice has been cloned?
Audio artifacts may sometimes exist, but listening carefully is not a reliable security method. If the call involves money, credentials or sensitive information, contact the person independently through a known telephone number.
How can I detect a deepfake video?
Visual inconsistencies can provide clues, but increasingly sophisticated deepfakes may not contain obvious artifacts. Verify the source, context and identity through another channel instead of relying exclusively on visual inspection.
What is AI phishing?
AI phishing uses generative artificial intelligence to help create, personalize, translate or automate fraudulent messages designed to steal credentials, information or money.
Are spelling mistakes still a good way to identify phishing?
No. Generative AI allows attackers to produce fluent and grammatically correct messages in many languages. Security decisions should focus on sender identity, URLs, context, requested actions and verification rather than grammar alone.
Can a video call be a deepfake?
Yes. AI systems can manipulate or synthesize video and audio, including increasingly convincing real-time impersonation. A video call should not be the sole verification mechanism for high-risk transactions.
What should I do if a relative calls asking for emergency money?
End the communication and contact that person using a telephone number you already know. If necessary, confirm the situation through another family member. Do not trust the voice alone.
How can businesses prevent AI impersonation fraud?
Organizations should use independent verification channels, multi-person payment approval, strict procedures for bank-detail changes, phishing-resistant authentication, employee training and clear escalation procedures for unusual requests.
The best defense against AI scams is not better eyesight
The quality of synthetic media will continue to improve.
Humans should not expect to win a permanent contest based on spotting strange pixels, unusual blinking or imperfect voices.
Those clues remain useful.
They are not sufficient.
The more robust response is procedural:
Stop.
Change channel.
Verify identity.
Verify the request.
Protect irreversible actions.
AI has increased the ability to manufacture convincing evidence.
Security therefore needs to rely less on appearance and more on authentication.
Signal detected.
Digital trust is moving from recognition to verification.
Monitoring continues.