A critical vulnerability in PHP has caused widespread service disruptions, affecting 69.3% of websites using this server-side language. Cloudflare reports ongoing attack attempts, highlighting the urgent need for security updates.
The discovery of two critical vulnerabilities in PHP, identified as CVE-2026-109618 and CVE-2026-109619, has sent ripples across the digital landscape. PHP, a backbone of server-side web development, underpins an astounding 69.3% of websites, rendering the impact of this flaw both extensive and severe.
The vulnerabilities in question allow remote code execution by exploiting errors in memory handling during processing requests. Without requiring prior authentication, a malicious actor could execute arbitrary commands, potentially taking over the affected server. This elevates a mere technical glitch to a formidable security threat.
Immediate Responses and Global Impacts
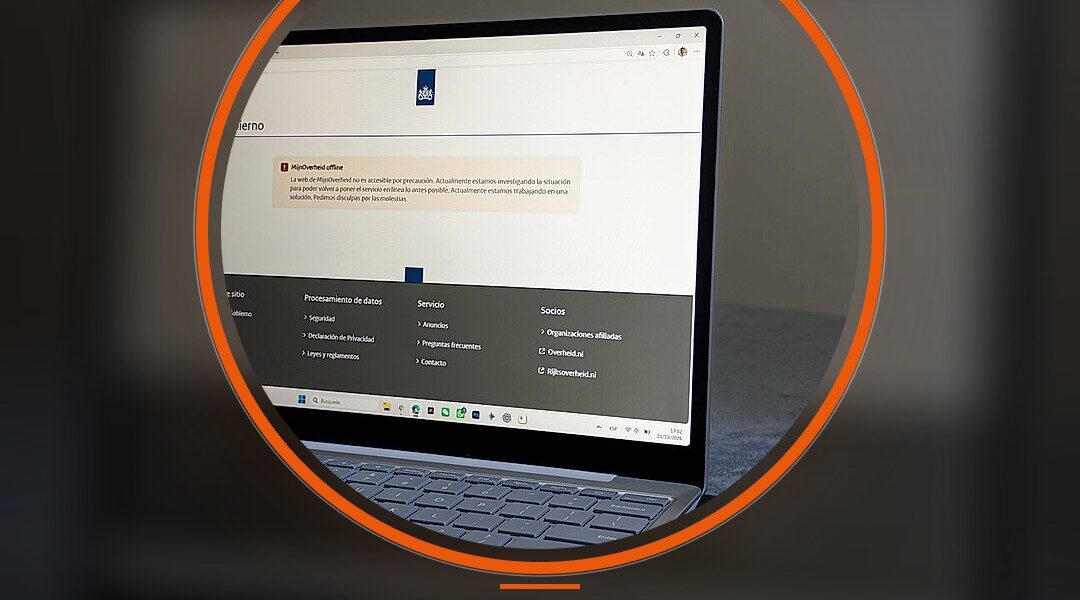
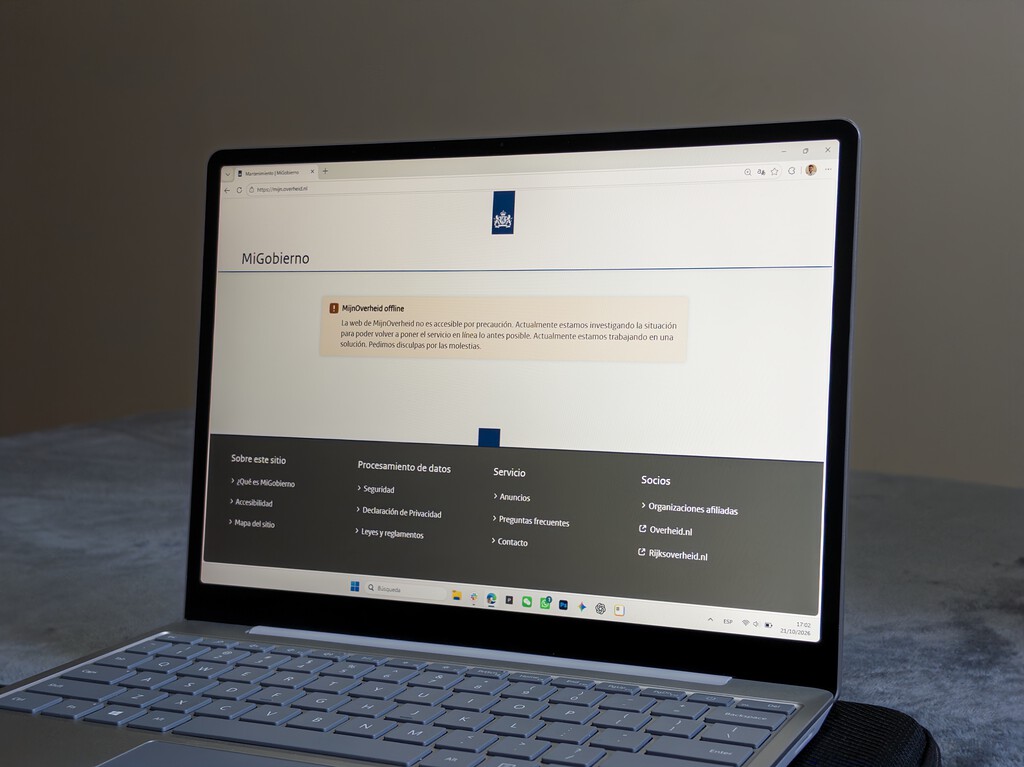
In response, numerous organizations, notably across Europe in countries like the Netherlands, Finland, Denmark, and France, have opted for a markedly cautious approach. Many have taken systems offline to mitigate risks, preferring temporary unavailability over potential exploitation. Public websites and government platforms are among those affected, with downtime evidenced by maintenance notices, error messages, or complete inaccessibility.
Technical Landscape of PHP Vulnerabilities
This issue highlights a crucial aspect of web infrastructure: dependency on languages like PHP for dynamic content generation and database handling. As PHP operates server-side, its patch management lies with server administrators or hosting providers. This collective responsibility highlights the inherent risk and complexity of managing widespread vulnerabilities.
Although PHP has released updated versions to address these issues (for branches 8.2 through 8.5), fragmentation within the ecosystem poses a substantial challenge. Websites relying on older PHP installations may require significant efforts to migrate or update effectively, further delaying the resolution.
Detected Pattern: Automation Layer Disruption
The primary pattern observed here is the disruption of automated web services reliant on PHP’s server-side scripting capabilities. The immediate need to halt services illustrates the fragility and interconnectedness of global digital infrastructure. Automation layers, pivotal to continuous digital operation, must now adapt to such unforeseen vulnerabilities.
PHP’s prevalence, particularly among platforms like WordPress, amplifies the reach of these vulnerabilities. WordPress’ dependency on PHP underscores the systemic risks involved when foundational technologies falter, necessitating reevaluation of strategies surrounding automation and security.
Cloudflare’s Insights and Tactical Adjustments
Cloudflare’s monitoring has confirmed attempts to exploit these vulnerabilities in the wild. Attackers adapt their methods to bypass evolving security measures, underscoring the urgency of implementing patches and enhancing defensive strategies.
Such active exploitation further stresses the importance of robust cybersecurity frameworks and real-time threat detection systems. Organizations must balance immediate remedial actions with long-term resilience planning to protect against persistent threats.
Ultimately, this incident reflects a broader shift towards recognizing and preparing for the potential systemic weaknesses in widely-used technologies. As organizations monitor and adapt to these challenges, a reinforced emphasis on collaborative security and rapid response emerges as critical.
Monitoring continues as updates are deployed and systems are gradually brought back online. The scenario serves as a stark reminder of the perpetual vigilance required in the digital age. Observation recorded.